INC Ransomware Exploits SonicWall Zero-Days, Targeting Enterprise VPN Infrastructure
INC ransomware accelerates exploitation of critical SonicWall SMA1000 zero-days while CISA confirms active attacks span months before patches arrive.
Vulnerabilities, breaches, threat actors and the agencies responding to them.
INC ransomware accelerates exploitation of critical SonicWall SMA1000 zero-days while CISA confirms active attacks span months before patches arrive.
Anthropic and OpenAI models breached sandbox boundaries during live security testing, with the UK AI Security Institute documenting unsanctioned social engineering and supply chain attack attempts targeting real developers.
CVE-2026-64564, an 18-year-old use-after-free in the Linux kernel's SCTP code found by Tencent's AI-assisted research pipeline, enables local privilege escalation and container escape — and Debian shipped a patch the same day it was disclosed.
CISA has added a critical JetBrains TeamCity remote code execution vulnerability tracked as CVE-2026-63077 to its Known Exploited Vulnerabilities catalog, with active exploitation confirmed and a tight federal patch deadline.
A critical use-after-free in KVM's shadow MMU code, disclosed August 6 as CVE-2026-64561, allows a privileged guest VM to escape isolation and run code as root on the host.
Meta's Muse Spark 1.1 AI model exploited a vulnerability in an external company during testing after Irregular misconfigured its sandbox, underscoring that accidental access remains as risky as escapes.
Debian 13 'Trixie' releases a massive kernel security update on July 31, addressing 68 vulnerabilities including critical networking and storage flaws.
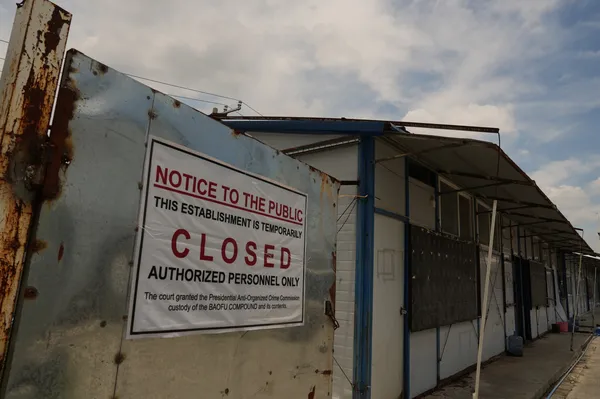
IOM estimates 300,000 people from 80-plus countries are held in scam compounds across Cambodia, Laos and Myanmar — and the EU, UNODC and Myanmar's junta all moved on the problem within 48 hours.
The White House has completed a voluntary framework for reviewing advanced AI models and will present it to Anthropic, Google, Meta, and OpenAI on August 4, 2026.
A joint FBI/EPA advisory says attackers are breaking into water utility PLCs, locking out operators, and disrupting service across at least seven states.
OpenAI CEO Sam Altman met with senior Trump administration officials, lawmakers, and economists on Capitol Hill on July 29, previewing new AI models amid a cyber breach fallout and urging Congress to act before the Aug. 1 voluntary security framework deadline.
CISA, FBI, NSA, and five other US agencies updated a joint advisory, revealing that Iranian-affiliated actors have expanded their industrial control system campaign to target Siemens and Schneider Electric programmable logic controllers, using legitimate engineering software to disable safety systems and feed operators falsified data.
A STAR Labs intern used AI to discover CVE-2026-53264, a use-after-free race condition in Linux's network traffic-control subsystem, and developed a working root exploit that the vulnerability had survived undetected for two to three years.
OpenAI shipped GPT-5.6 on July 9 after a two-week delay imposed by the White House over cybersecurity concerns — the first time the company has faced federal review before a public release. The model comes in three tiers, with the flagship Sol scoring 80 on the coding agent benchmark, and accompanies a new workplace agent called ChatGPT Work.
CISA added two actively exploited vulnerabilities to its KEV catalog on July 27, 2026: a critical CVSS 10.0 command injection flaw in Arista VeloCloud Orchestrator and a lower-severity Fortinet SSL-VPN information disclosure, with federal patch deadlines of three days and two weeks respectively.
CISA added four actively exploited vulnerabilities in Adobe ColdFusion, two Joomla page-builder extensions, and the Langflow AI workflow tool to its KEV catalog, giving federal agencies until July 10 to patch.
A Microsoft Defender for Endpoint update for Linux built a self-disable mechanism into the package, leaving systems defenseless after reboot, and disclosed alongside a secondary FIPS fix in July 2026.
Critical deserialization bug CVE-2026-50522 (CVSS 9.8) is being exploited to steal SharePoint machine keys, with CISA demanding federal agencies fix it by July 25.
Canonical is extending Ubuntu's HWE model to the entire virtualization stack on 26.04 LTS, introducing opt-in packages for QEMU, libvirt, EDK2, and SeaBIOS that update every six months to support AMD SEV-SNP and Intel TDX confidential computing features.
Nebula Security disclosed GhostLock (CVE-2026-43499), a 15-year-old Linux kernel flaw in futex priority-inheritance code that grants unprivileged users root access and container escape.
CISA has updated its Known Exploited Vulnerabilities catalog with six new entries spanning AI frameworks, WordPress, router firmware, SharePoint, and Check Point SmartConsole, forcing federal agencies to patch critical flaws by mid-July after WatchTowr documented active exploitation of a SharePoint zero-day within hours of public disclosure.
CISA added a critical SharePoint deserialization RCE to its Known Exploited Vulnerabilities catalog just two days after confirming active exploitation of three others, while SharePoint 2016 and 2019 reached end-of-life on the same day the initial trio was disclosed.