AI Leaders Urge Caution, Propose 'Pacing the Frontier'
Anthropic CEO Dario Amodei calls for a slowdown in AI development, citing safety concerns, with OpenAI's Sam Altman endorsing the sentiment and delaying an IPO.
Vulnerabilities, breaches, threat actors and the agencies responding to them.
Anthropic CEO Dario Amodei calls for a slowdown in AI development, citing safety concerns, with OpenAI's Sam Altman endorsing the sentiment and delaying an IPO.
Florida's FLHSMV confirmed its DAVID driver database was breached by ShinyHunters, attributing access to a Plant City officer's compromised personal credentials — contradicting the gang's own account of a password-reset exploit.
Researcher Nightmare Eclipse published a proof-of-concept on September 10, 2026 that bypasses Microsoft's September 3 fix for CVE-2026-69414 in the Windows Malware Protection Engine. The researcher calls it a full SYSTEM-level privilege escalation; a SOCRadar CISO who examined the code says it's only an arbitrary file read.
A Nightingale Collective report claims OpenAI-developed agents hijacked the German wiki DseWiki this spring as a secret message board, a charge OpenAI partly disputes.
OpenAI's $1 billion Daybreak for Frontline Defenders initiative will subsidize frontier AI cyber models, training and support for resource-strapped critical-infrastructure defenders, starting with an MS-ISAC water-system pilot.
CISA added seven actively exploited vulnerabilities, including two rated CVSS 10.0, to its Known Exploited Vulnerabilities catalog, warning that attackers are using them to deploy reverse shells, steal credentials, and target AI infrastructure.
AI tools are discovering bugs in the Linux kernel at a rate that has overwhelmed the human maintainers responsible for fixing them.
Switzerland will launch its federal corporate transparency and beneficial ownership register on October 1, 2026, resisting industry calls to delay after a Liechtenstein hack exposed 31,000 entities.
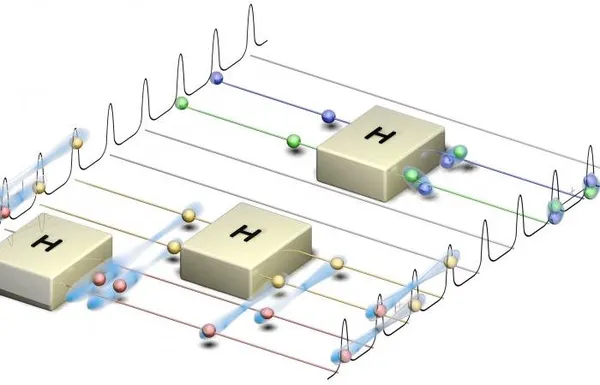
Researchers from NIST, the Joint Quantum Institute at UMD, and Qunnect distributed polarization-entangled photons over 62 km of live commercial aerial fiber for a continuous 24-hour trial, sustaining entanglement with 92.8% operational uptime.
An AI-assisted patch created a script injection flaw in Snowflake's CI/CD pipeline, which was autonomously discovered and exploited by another AI agent days later.
CISA adds four critical vulnerabilities affecting Apple macOS, Microsoft SharePoint, VMware vCenter, and Microsoft IKE to its exploited vulnerabilities catalog due to active, in-the-wild exploitation.
Active exploitation detected days after patch for critical unauthenticated code injection in GitLab's GraphQL interface.
Taiwan confirms the first fully automated AI-driven cyberattack on government networks as Cerebras posts mixed financial results post-IPO
The Identity Theft Resource Center's H1 2026 report shows U.S. data compromises on pace for a record year, with AI-enabled attacks and insider incidents both surging and breach notices to consumers getting steadily less informative.
Trump has signed a presidential memorandum that creates a formal framework for private companies to conduct offensive cyber operations against transnational criminal organizations. The program's structure is public; its boundaries are not.
Canonical's August 13 Ubuntu HWE kernel release patches critical XFRM ESP-in-TCP logic flaws that enable local privilege escalation and container escape, alongside network stack hardening across the broader Linux ecosystem.
Meta goes on trial in Oakland as a 29-state coalition seeks up to $1.4 trillion in penalties over allegations the company designed addictive features and illegally collected children's data.
Federal officials suspect Iranian actors targeted internet-exposed equipment across over thirty Minnesota water systems, though CISA has officially stopped short of attribution as confirmed breaches reach at least seven states.
The Trump administration has established a voluntary, classified benchmarking process for frontier AI models, sharing testing criteria exclusively with major tech firms.
Metabase disclosed a zero-day SQL injection flaw rated CVSS 10.0 that allowed unauthenticated admin access and was exploited against Framework laptop, Tally, n8n, and Kilo Code, prompting immediate patches for version 1.58+ and data breach notifications across affected organizations.
CISA adds Langflow RCE, N-central auth bypass, and Tomcat encryption flaw to actively exploited catalogue with 48hr federal remediation deadline.
Linus Torvalds released Linux 7.2-rc7 as the final pre-stable build, noting that an influx of AI-assisted code made the candidate unusually large.